
When using AAD cloud only PC´s and need to connect to on-premise resources. Azure AD Kerberos is needed. And it´s so simpla to enable now adays. When Enabled you can get SSO to internal resources with FIDO2, Microsoft Authenticator Passwordless and Windows hello for business.
Enable Azure AD Kerberos
- Open a PowerShell prompt using the Run as administrator option.
- Install the Azure AD Kerberos PowerShell module by running:
Install-Module -Name AzureADHybridAuthenticationManagement -AllowClobber- Run the following PowerShell commands to enable Azure AD Kerberos and create a Server object both in your on-premises Active Directory domain and in your Azure Active Directory tenant:
$domain = $env:USERDNSDOMAIN
$userPrincipalName = "administrator@contoso.onmicrosoft.com"
Set-AzureADKerberosServer -Domain $domain -UserPrincipalName $userPrincipalName
That’s it folks! So simple!
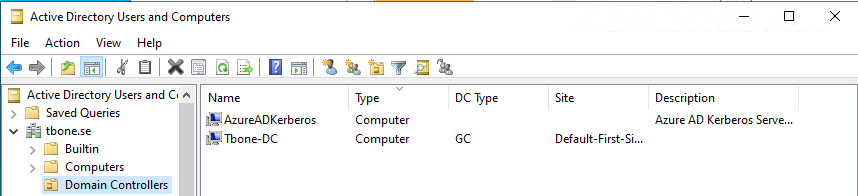
Now you will have a new server object in your domain controller OU that represents Azure: